Cybersecurity Awareness Month: Protecting Your Business
Cybersecurity is not only a concern for large companies. Businesses of all sizes use technology to store customer details, accept payments, communicate with employees, and manage essential day-to...
Read more
Back-To-School Safety Reminders
As families get ready for another school year, it’s the perfect moment to refresh the everyday safety habits that help keep students protected. From the commute in the morning to after-school...
Read more
Insurance & College Students - Key Considerations
Sending a child to college marks an important turning point, full of excitement, new routines, and growing independence. While academics, housing, and financial planning often take center stage,...
Read more
Does Auto Insurance Follow the Car or the Driver?
If you’ve ever lent out your car—or borrowed someone else’s—you may have wondered which insurance policy takes the lead if an accident happens. Although most situations follow a predictable pattern...
Read more
Boat Liability Risks Most Owners Don’t Think About
Boating season brings excitement, long-awaited sunshine, and plenty of time on the water. But before launching for the first outing of the year, it’s important to confirm that your insurance policy...
Read more
Pool, Trampoline & Backyard Liability - Are You Covered This Summer?
Summer often inspires homeowners to turn their outdoor spaces into lively gathering spots, adding features like pools, trampolines, and play structures to create a fun environment for family and...
Read more
What Is an Additional Insured Endorsement?
Additional insured endorsements are a common requirement in commercial agreements, but they are often misunderstood. While they can offer valuable protection when businesses work together, the...
Read more
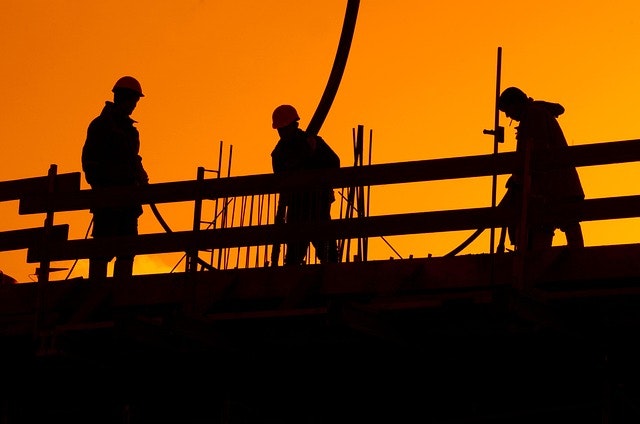
Rising temperatures can create serious challenges for businesses that rely on physical labor, especi...
Rising temperatures can create serious challenges for businesses that rely on physical labor, especially in industries like construction, agriculture, manufacturing, and other hands-on fields. As...
Read more
Summer fun tends to arrive quickly, and once the warm weather hits, weekends often book up with outd...
Summer fun tends to arrive quickly, and once the warm weather hits, weekends often book up with outdoor plans before you know it. Whether you're heading out with an RV, launching a boat, riding...
Read more
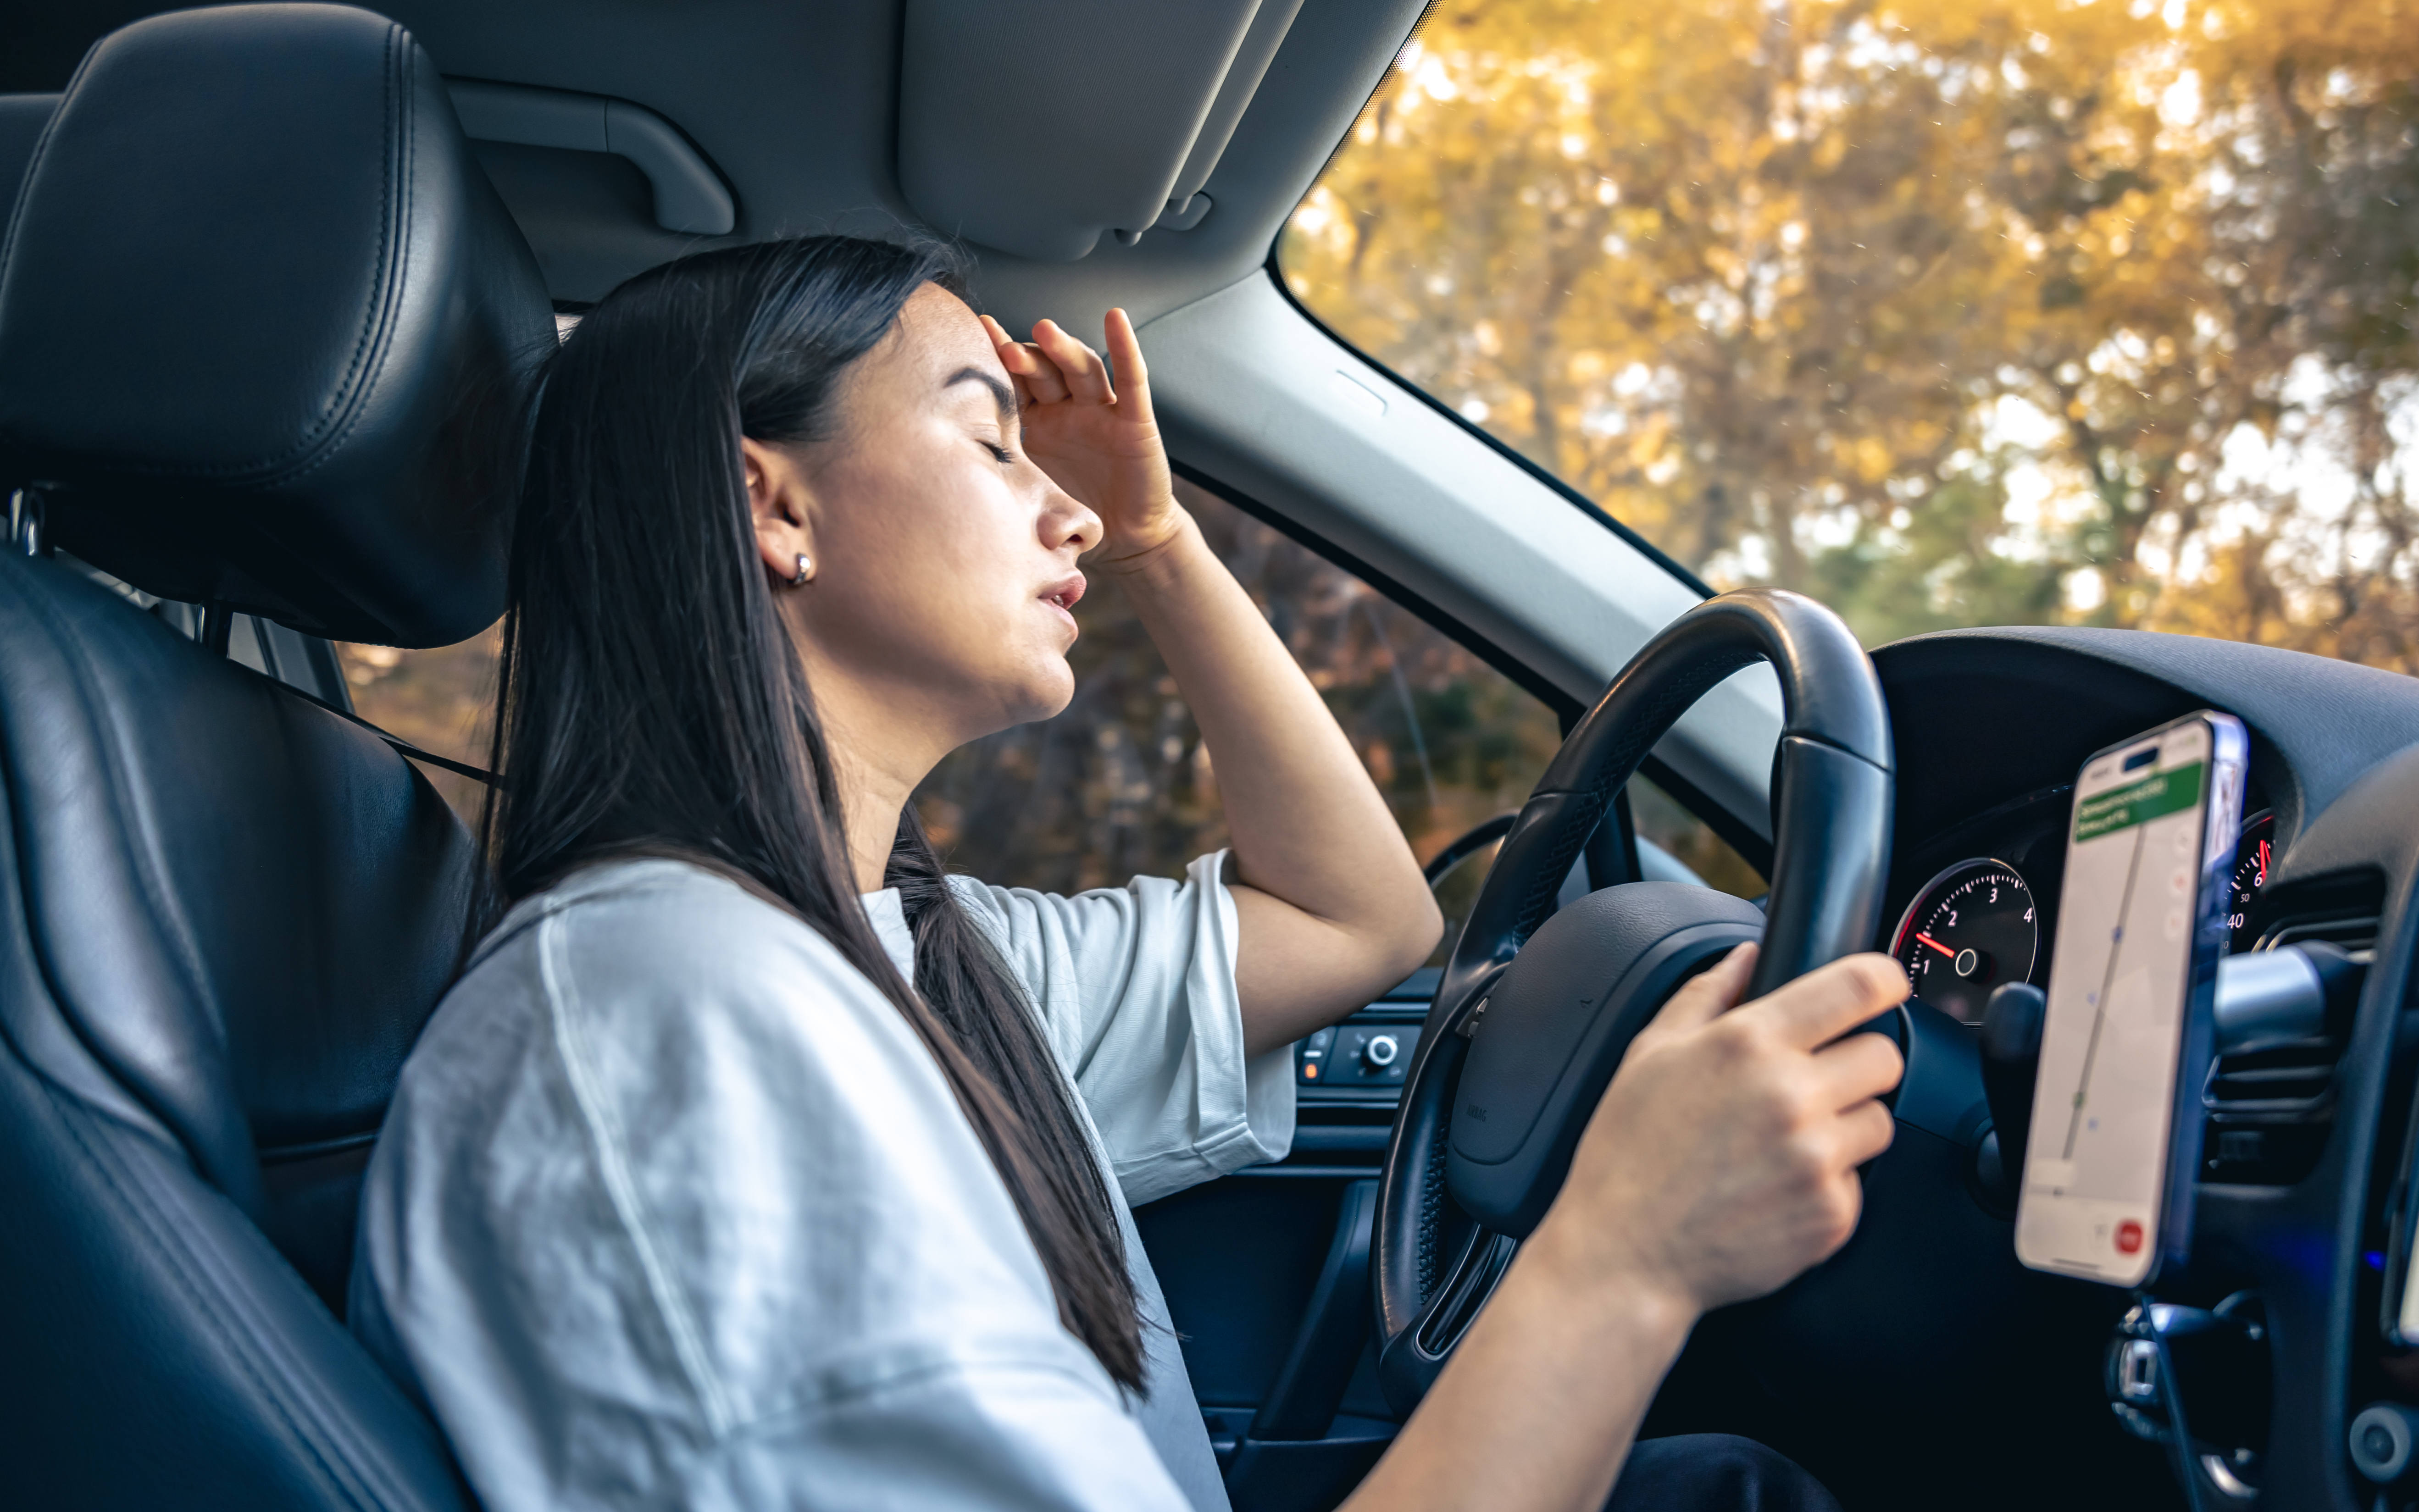
April marks Distracted Driving Awareness Month, a reminder of how quickly small lapses in focus can...
April marks Distracted Driving Awareness Month, a reminder of how quickly small lapses in focus can turn into major dangers on the road. Many collisions happen not because of road or weather...
Read more
As spring arrives and winter wraps up, it’s an ideal moment for commercial property owners to get ah...
As spring arrives and winter wraps up, it’s an ideal moment for commercial property owners to get ahead on seasonal upkeep. A thoughtful maintenance plan now can help prevent expensive repairs,...
Read more
8 Common Insurance Myths That Could Leave You Unprotected
March 11th is Debunking Day, making it the perfect opportunity to clear up some long‑standing misconceptions about home and auto insurance. Many people base their decisions on outdated assumptions...
Read more
Essential insurance questions every small business should understand
Running a small business involves countless decisions, and choosing the right insurance is often one of the areas that creates the most uncertainty. Whether you are opening your doors for the first...
Read more
Safeguarding Your Valentine’s and Presidents’ Day Purchases
February may be the shortest month of the year, but it often brings a surprising number of big purchases. From Valentine’s Day jewelry and meaningful keepsakes to Presidents’ Day car deals and long...
Read more

Key Motorcycle Accident Stats and Safety Tips
There's a unique thrill and sense of freedom that comes with riding a motorcycle. However, it's crucial to acknowledge the inherent risks that accompany the joy of riding. Understanding key...
Read more
Smart Steps to Protect Your Holiday Valuables
The holiday season is filled with excitement—unwrapping thoughtful gifts, creating memories with loved ones, and treasuring the special items that make this time of year feel magical. With the...
Read more
Essential Tips for Winter Home Prep
Prepare Your Home for Winter BlissAs winter approaches, the chill in the air is a timely reminder to ensure our homes remain safe and cozy during the colder months. A bit of preparation today can...
Read more
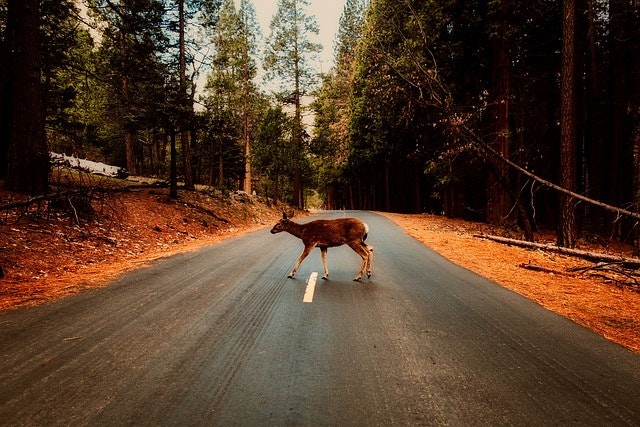
Prepare for Deer Season: Safety Tips for Drivers
As the vibrant hues of fall paint our landscapes, it’s easy to get lost in its beauty. However, this season also brings hidden dangers, particularly in the form of increased deer-related accidents....
Read more
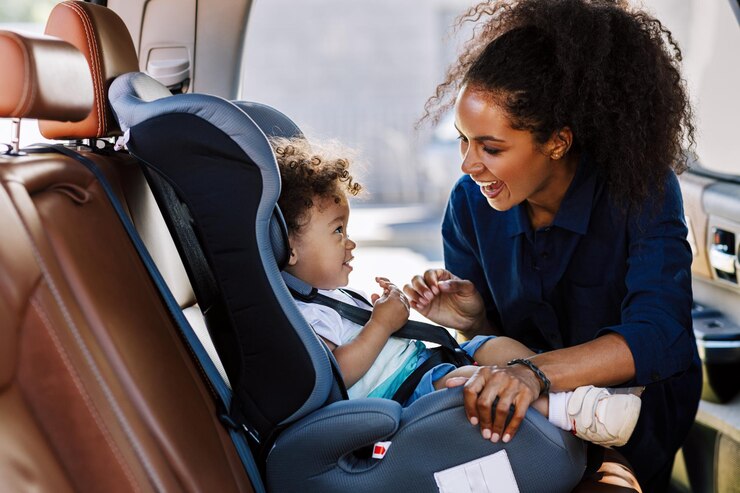
Ensuring Car Seat Safety During Child Passenger Safety Week
As a parent or caregiver, nothing is more important than a child’s safety, especially when traveling in a car. With Child Passenger Safety Week from September 21–27, now is the perfect time to...
Read more
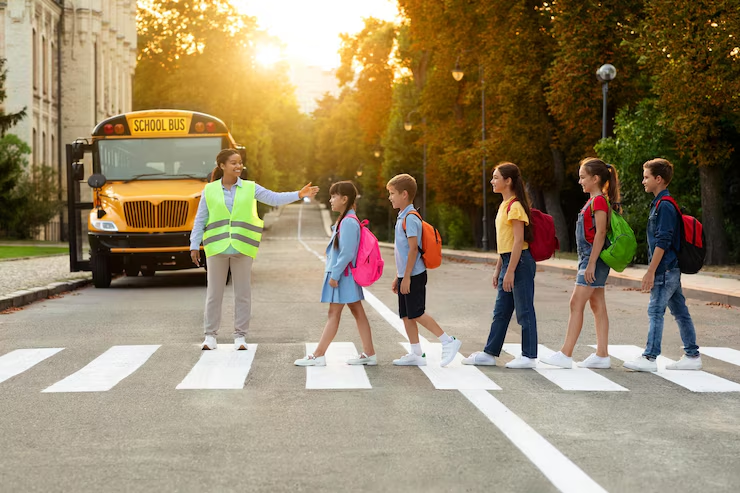
Back-to-School Safety: National Traffic Awareness Month
Ah, August—the time of year when families pack up summer fun and gear up for a new school year. As backpacks are filled and lunchboxes prepped, there's a palpable mix of excitement and stress in...
Read more

What Insurance Does My Washington LLC Actually Need?
Establishing an LLC in Washington might seem like a complete solution for liability protection, but it isn't the entire picture. Though an LLC can separate your personal assets from business...
Read more

Do I Need Earthquake or Flood Insurance for My Home in Southwest Washington?
Coverage Gaps in Standard Homeowners InsuranceMany homeowners mistakenly believe that their standard home insurance policy covers natural disasters such as earthquakes and floods. However, typical...
Read more
How Long Do I Have to Keep an SR-22 in Washington?
Understanding SR-22 Requirements in WashingtonSR-22 insurance is sometimes misconceived as just another type of insurance. However, it's essential to understand that an SR-22 is actually a...
Read more
View more